Automated Cookie Extraction & Tunneling
Extract, decrypt, and tunnel fresh c_user, xs, and datr authentication cookies into persistent sessions without triggering checkpoints.
Technical Specifications & Parameters
Architectural Overview
Step-by-Step Operation Guide
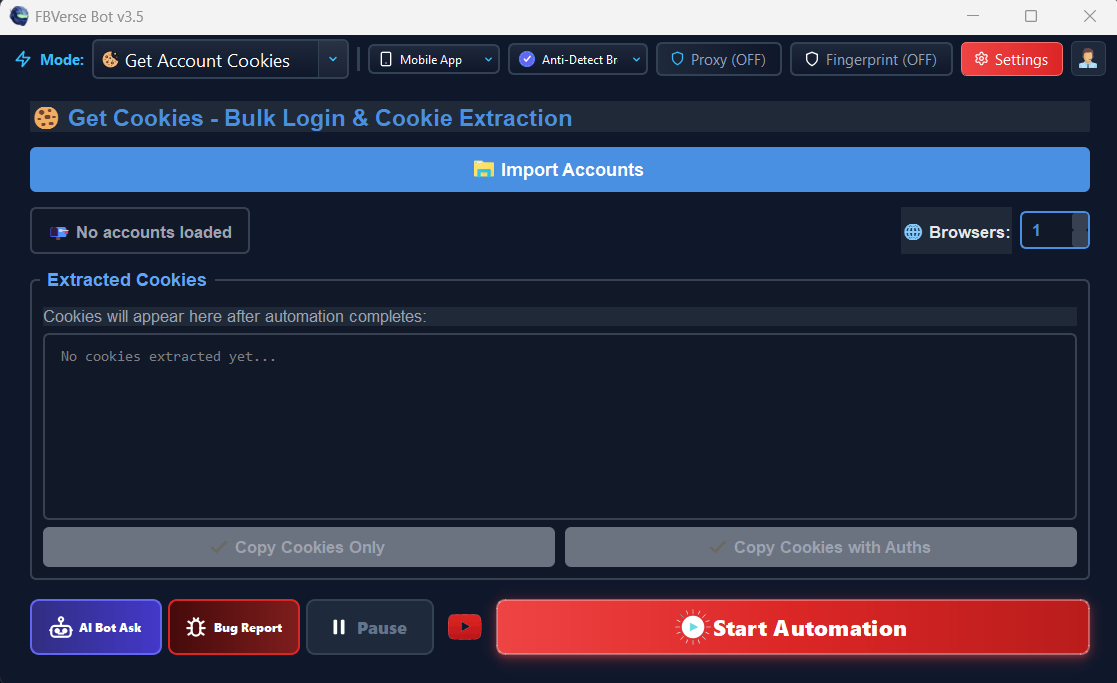
Open the "Get Cookies" tab in FBVerse Bot v3.5.
Select active browser windows or load account credentials.
Click "Batch Extract Cookies" to capture active authentication strings.
Run the validity validator to ensure all extracted cookies are in "Live" status.
Export cookies as JSON or inject them into anti-detect profiles for instant access.
Strategic Advantages
Bypasses suspicious login notifications and device recognition prompts.
Allows team members and resellers to access accounts without sharing passwords.
Instantly detects invalid or checkpointed accounts before starting listing runs.
Simplifies account backup and rapid session swapping.
Frequently Asked Questions
How long do extracted cookies remain valid?
As long as the account does not click "Log Out of All Sessions", cookies typically remain active for 30-90 days.
Can I import cookies purchased from PVA account sellers?
Yes. FBVerse Bot parses standard JSON and string format cookies from all major account sellers.
Does extracting cookies trigger Facebook security alerts?
No. The extraction reads the session cache directly from memory or the browser SQLite storage without network calls.
Ready to deploy Automated Cookie Extraction & Tunneling?
Get instant access to this feature along with all 16 enterprise modules in the latest FBVerse Bot v3.5 release.
Explore More v3.5 Innovations
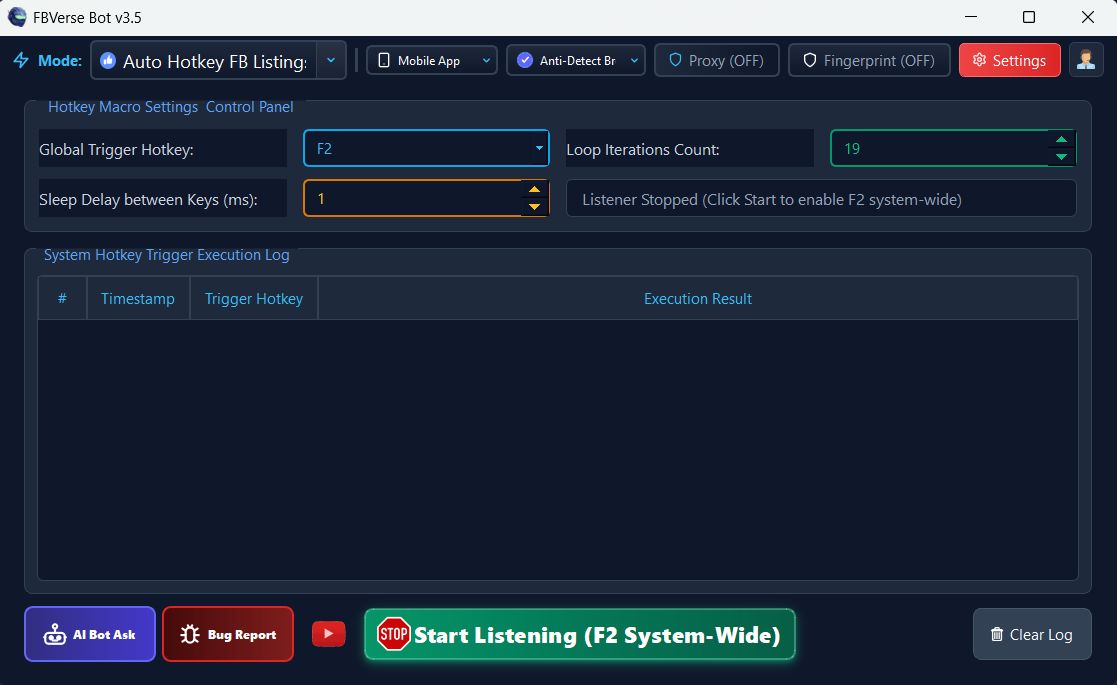
F2 Hotkey Instant Listing Renewal
Renew active Facebook Marketplace listings instantly with a single F2 keystroke without logging out or refreshing sessions.
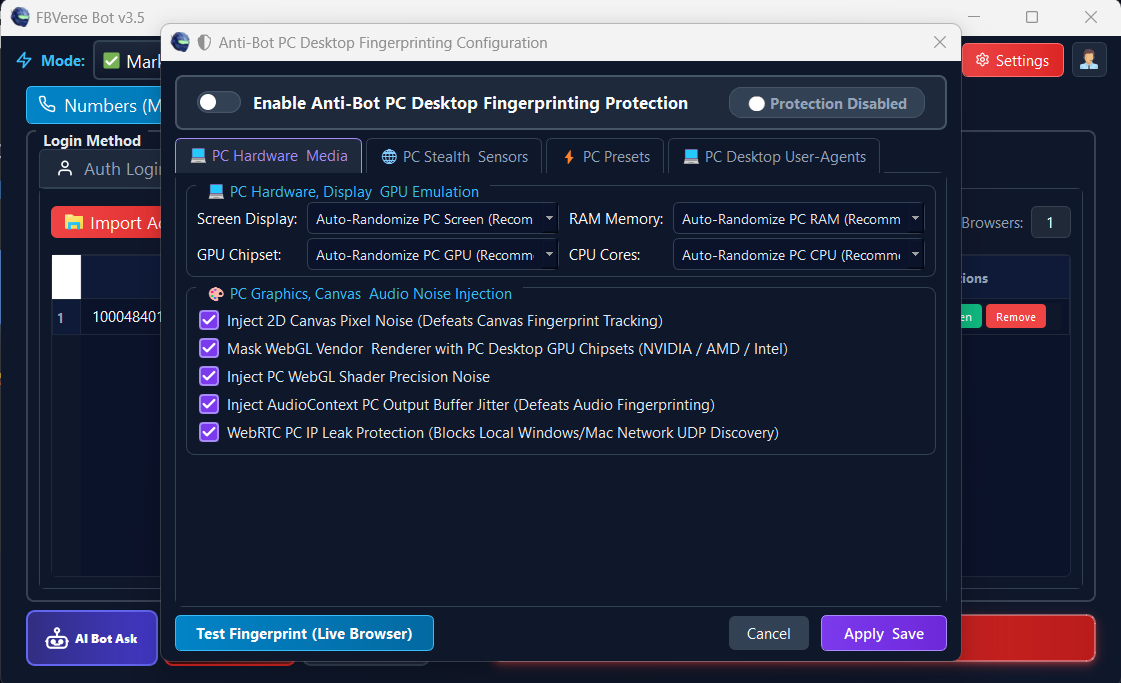
Advanced Anti-Bot Fingerprint Protection
Spoof Canvas, WebGL, AudioContext, Font enumeration, and ClientRects to completely bypass Meta detection.
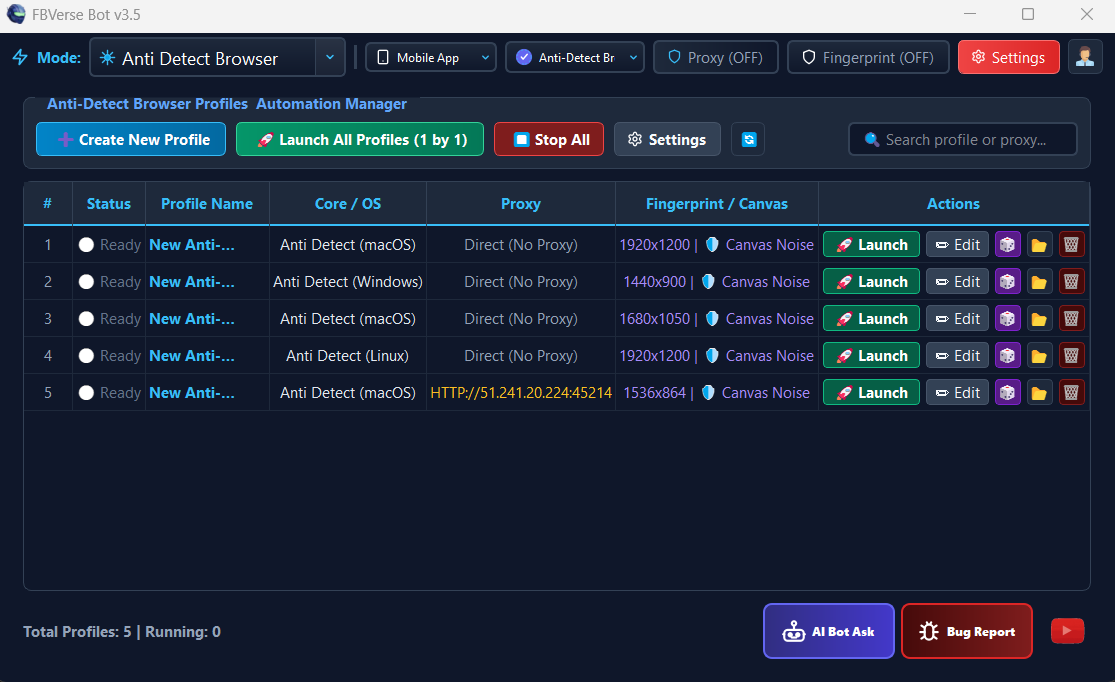
Anti-Detect Browser with Unlimited Profiles
Isolated multi-profile browser environment running unlimited independent Facebook sessions with dedicated proxy tunneling.